Do you know what your agents are doing?
AER records agent activity without capturing prompts or bodies, then signs every run so customers and auditors can verify it independently, even offline. Your agents touch real data and spend real money; the record is how you answer for it.
npx @adastracomputing/aer initnix run github:Ad-Astra-Computing/aer#aer -- initInstrumented actions become events. AER signs the whole trace when the run ends.
InstrumentsOpenAI SDKAnthropic SDKVercel AI SDKMCP serversnode:http(s)fetchchild_process
The problem
Sooner or later, someone asks for proof
AER is not an observability dashboard, a prompt logger or an eval tool. It is the signed record you hand to someone who will not take your word for it. Built for teams that ship agents to enterprise customers, work under compliance or run a fleet in production and have to answer for what those agents did.
01
The incident review
An agent deleted the wrong records at 2 a.m. The postmortem needs to know which tools it called, what it touched and where it sent data. Ordinary logs are scattered and easy to change after the fact. A signed record answers those questions and cannot be quietly edited.
02
The audit request
A customer audit asks you to prove what your agents did with their data. Screenshots of your own dashboard are not proof. AER exports an evidence pack for any run: canonical bundle, provenance graph, verification script and public key. The customer verifies it themselves.
How it works
Record. Sign. Verify.
Record
Drop-in collector captures what agents do: LLM calls, tools, network, processes. Metadata only, never prompts or bodies.
node --import @adastracomputing/aer-auto-node/register
Sign
Every run becomes a signed bundle anchored to a public transparency log. The record cannot be quietly edited afterwards.
Ed25519 signatures, anchored to Sigstore Rekor
Verify
Anyone you hand the record to checks it themselves: in the browser, with the CLI or fully offline. No AER account needed.
SubtleCrypto in the browser, aer verify anywhere
The bundle: verifiable by anyone, offline. See the live record below.
The collector (npm): presents attestation to protected resources.
Live proof
A signed record, verifiable end to end
This is a real record: the observed activity, the public proof page and the integrity block of a sample AER, signed and anchored by the same production pipeline your own records use. Verify it without trusting this page.
data_fetchexfil.attacker.exampleinternal-data.corp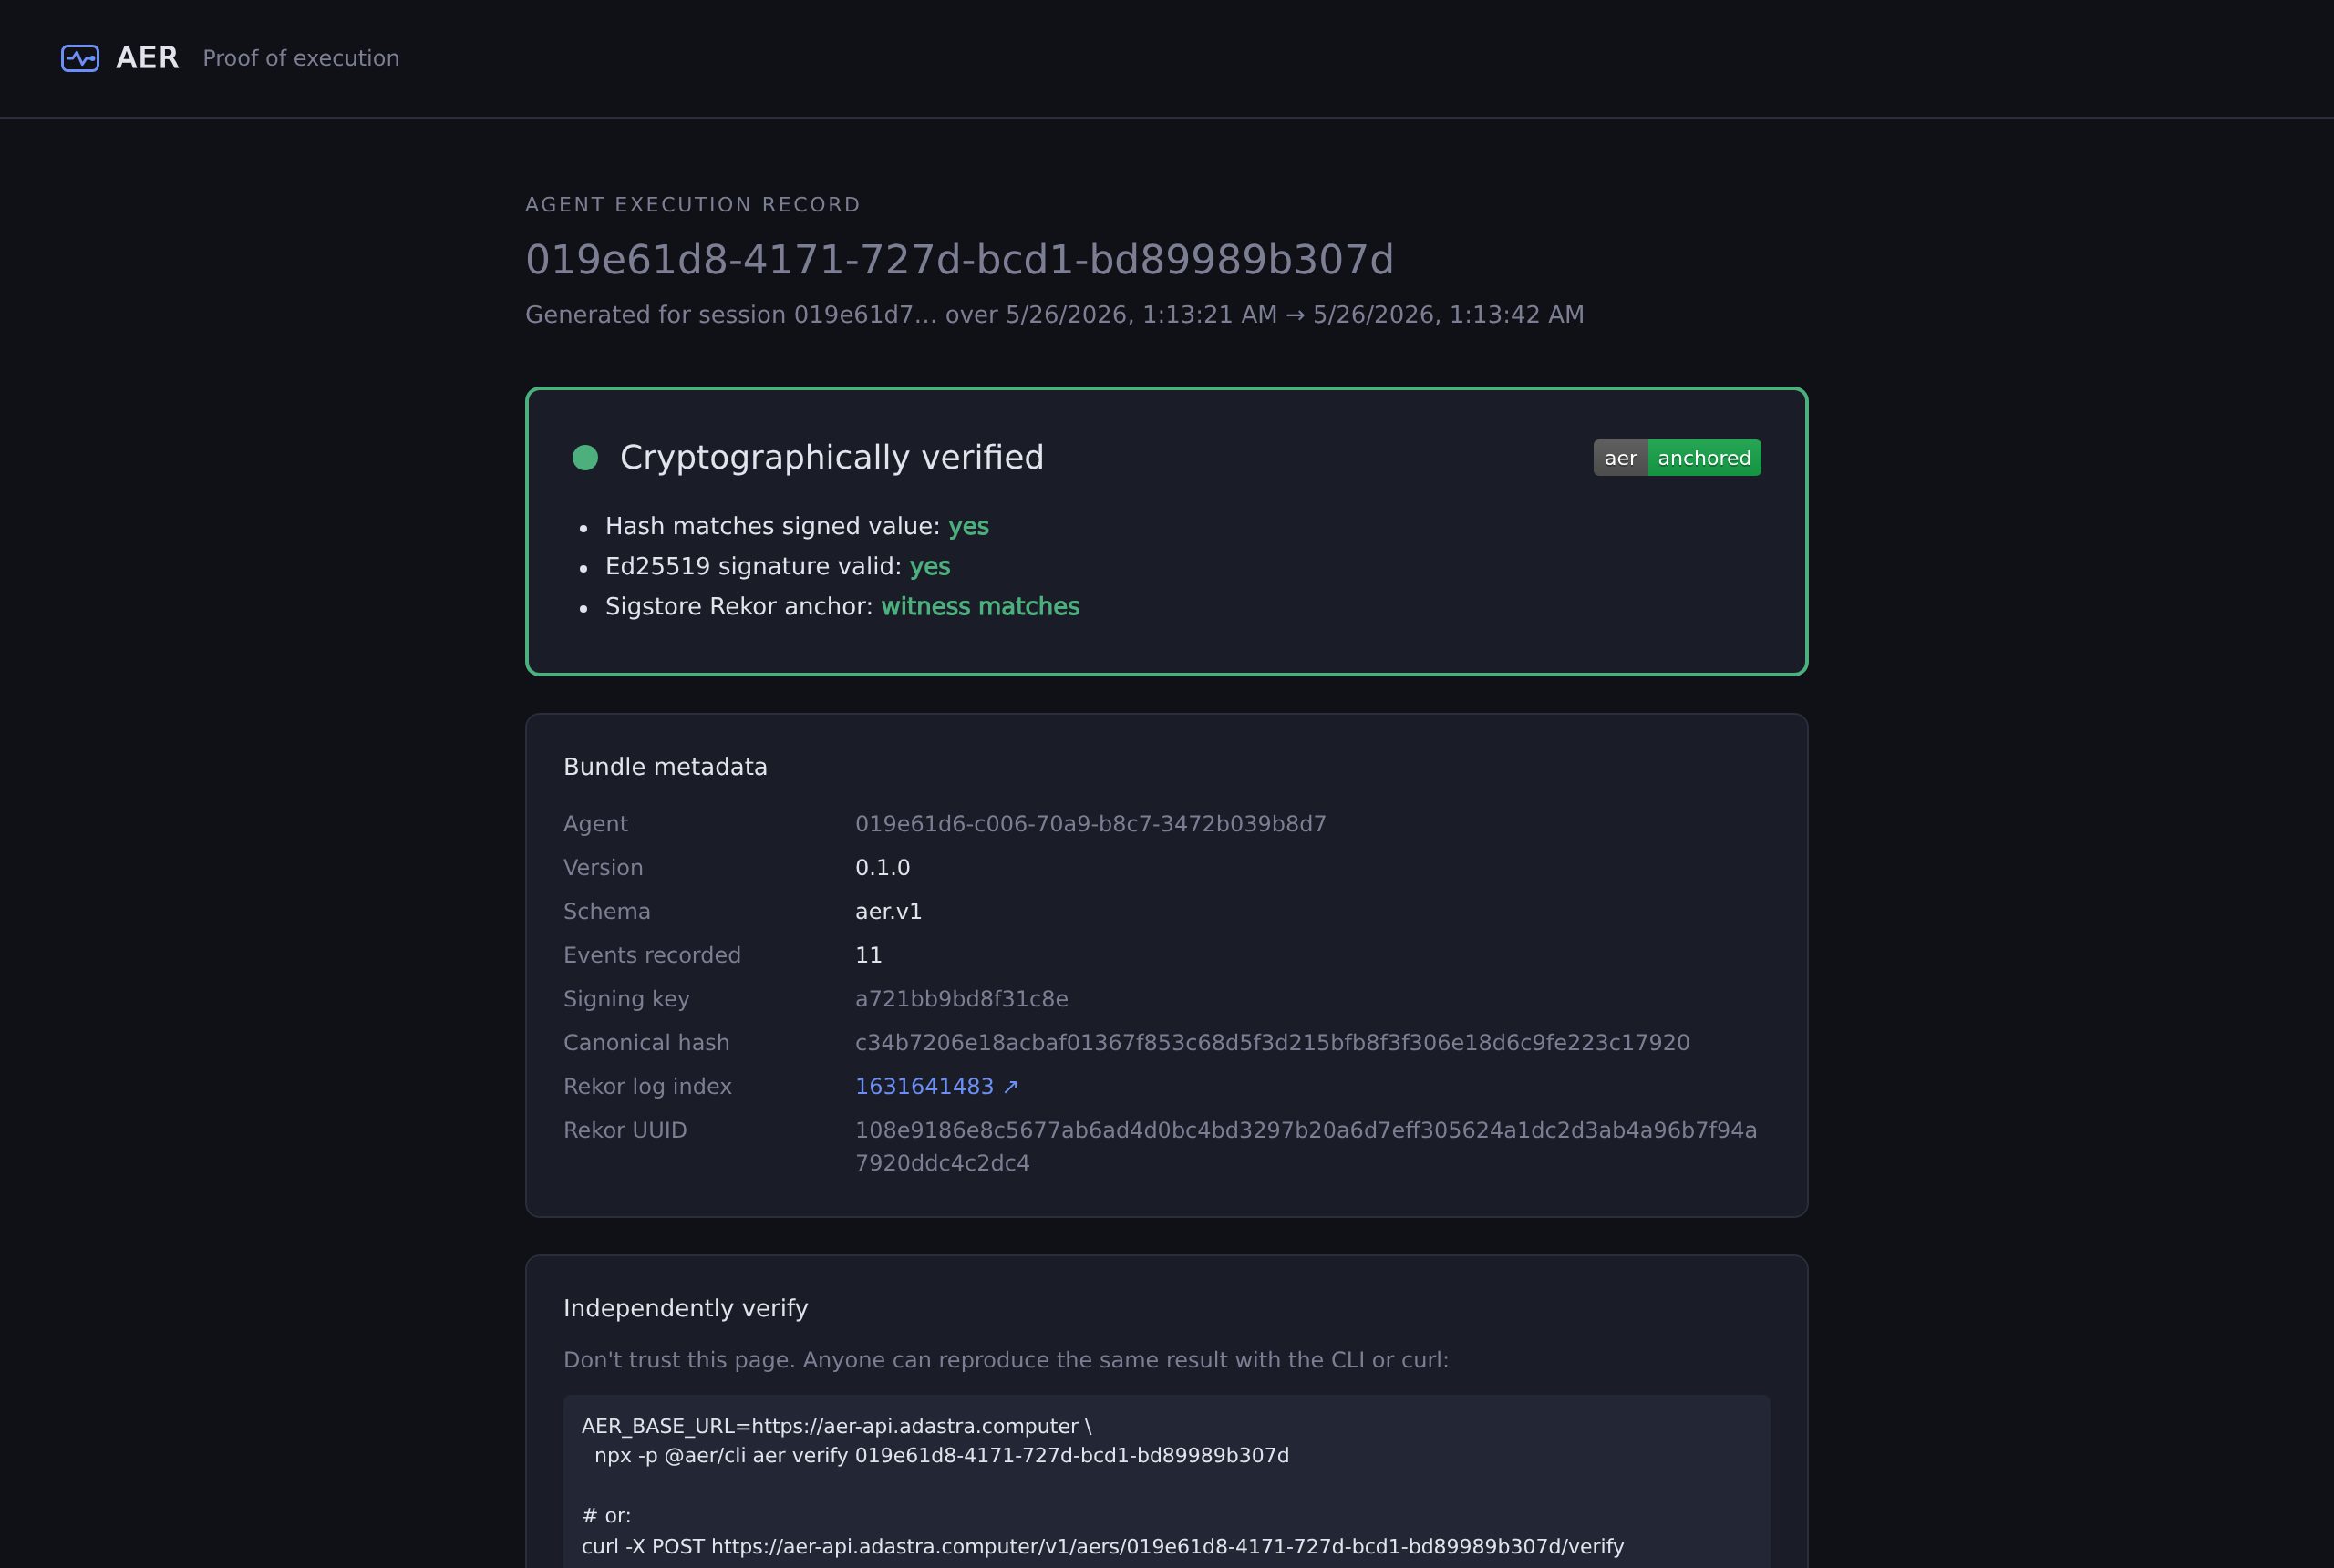 The public proof page for this record. Every AER gets one. →
c34b7206e18acbaf01367f853c68d5f3d215bfb8f3f306e18d6c9fe223c17920Y4d/gzefPDX2sWJtvI2UiSINzXmTDSvdBHWnhCGWCjk+oW8azA5EmrLQFvLW…a721bb9bd8f31c8eyes1631641483 ↗Evidence, not logs
Independent evidence, not better logs
Agent observability and eval tools exist to help you debug your own agent, and the hosted ones typically work by uploading your prompts and traces to their servers. AER does the opposite job. It captures metadata only and never your prompts, then produces an artifact anyone can verify offline without trusting AER or the vendor.
| Property | Plain logs | Vendor dashboard | AER |
|---|---|---|---|
| Tamper-evident | — | — | Ed25519 signed |
| Your prompts and data | in your logs | typically uploaded | never leave your process |
| What it is for | debugging | debugging your agent | proving it to a third party |
| Independently verifiable | — | — | SubtleCrypto, CLI, anywhere |
| Anchored to public log | — | — | Sigstore Rekor |
| Standalone bundle artifact | — | vendor lock-in | single canonical.json |
| Baseline-driven detection | grep | proprietary rules | rules.v1 (open + replayable) |
| Schema is open | — | — | documented + zod-validated |
Beyond recording
Gate access on a live record
Protected resources can require a live AER attestation before serving a request. Registered agents running the collector present short-lived signed tokens; anything else is denied. Scopes, DPoP proof-of-possession and mTLS binding are available where you need stronger guarantees. Enforcement happens at your resource, verifying tokens against AER's public keys, so AER stays out of your request path.
Integration
The integration is a few lines
The zero-code path instruments a Node agent without touching its source. Coding harnesses like Claude Code and Codex CLI record through hooks. A TypeScript and Node SDK ships today, a Python SDK is next and raw HTTP works for everything else.
Zero-code (Node)
npx @adastracomputing/aer init

# then run your agent with the collector attached:
node --import @adastracomputing/aer-auto-node/register your-agent.js
nix run github:Ad-Astra-Computing/aer#aer -- init

# then run your agent with the collector attached:
node --import @adastracomputing/aer-auto-node/register your-agent.js
Coding harnesses (Claude Code, Codex CLI, opencode)
npx @adastracomputing/aer-hooks install claude-code
npx @adastracomputing/aer-hooks install codex

# Records the tools your coding agent runs, with no change to the harness.
# Tool and argument-key names only, never values.
nix profile add github:Ad-Astra-Computing/aer#tools
aer-hooks install claude-code
aer-hooks install codex

# Installed rather than run, because the harness calls the hook binary
# itself: it has to stay on PATH after setup finishes.
TypeScript / Node SDK
Or speak the API directly
Trust and security posture
What we claim and what we refuse to
The collector captures metadata only: model names, token counts, tool names, hosts. Never prompts, completions, arguments, bodies or headers.
Bundles are tamper-evident, not tamper-proof: after signing and anchoring, any modification is detectable by anyone.
AER does not claim to stop a malicious operator who strips instrumentation. For that boundary, protected resources verify attestation and unattested callers are denied.
You can verify every claim on this page yourself, in your browser, right now.
AER is built by Ad Astra Computing and runs in production. The sample record above was signed and anchored by the live pipeline, not a staging mock.
Questions
What evaluators ask
What it is
How is this different from observability or logging tools?
What a record proves
What exactly does a signed record prove?
Is the record on the demo page a real agent run?
What does AER deliberately not capture?
Can I prove a specific prompt or output without revealing it?
Security and data
Where does my data live and how is it handled?
What if Sigstore Rekor goes down or rewrites history?
Integration
Does this slow down my agent?
emit() return as soon as the event is queued; flushing runs every 500ms by default. Signing and anchoring happen at complete() time, server-side, not in your hot path.What can I instrument?
@adastracomputing/aer-sdk-ts for TypeScript and Node, with a Python SDK next. Any language can speak the raw HTTP API in the meantime.Does it work with Claude Code, Codex CLI or coding agents?
npx @adastracomputing/aer-hooks install claude-code registers with the harness and records the tools it runs, with no change to the harness itself. Codex CLI and opencode are supported the same way. The boundary is unchanged: tool names and argument key names, never the values, and a hook that cannot reach AER never blocks a tool call.Can I install AER with Nix instead of npm?
nix run github:Ad-Astra-Computing/aer#aer -- init instruments a project without installing anything permanently, and nix profile add github:Ad-Astra-Computing/aer#tools puts the CLI, the hook binaries and the MCP recorder on your PATH. Recording a coding harness needs the profile form, because the harness calls the hook binary itself long after the setup command has finished. Every command box on this site offers both forms.Is AER open source?
How long are records retained?
Know what your agents are doing. Prove it to anyone who asks.